
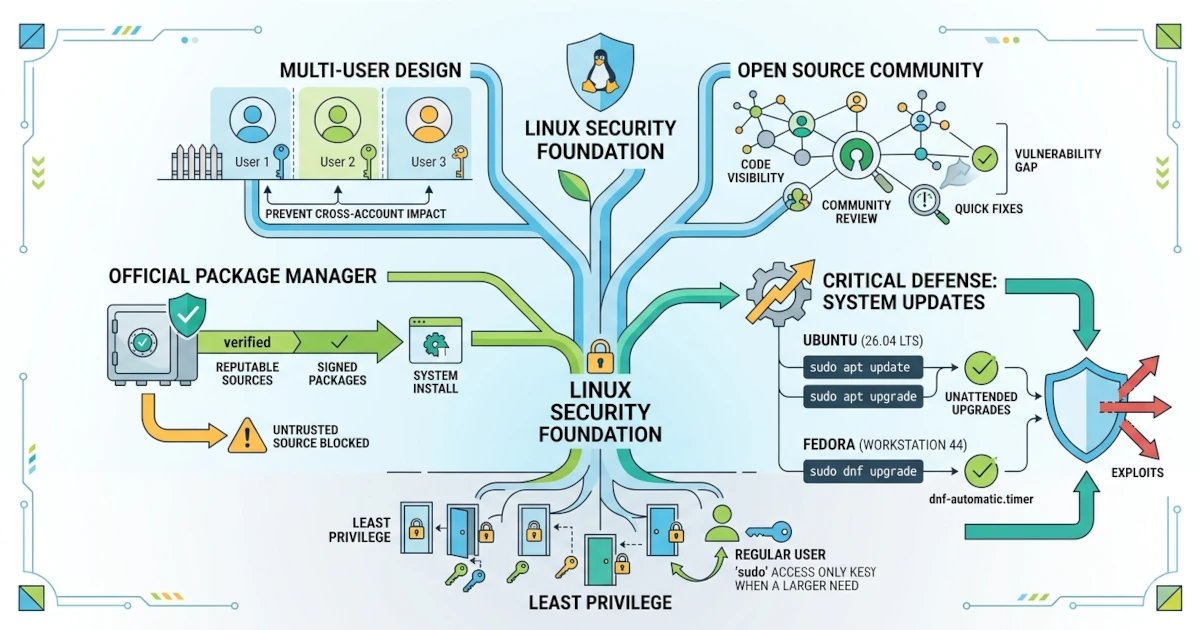
Security is one of the compelling reasons why many people choose Linux. However, security is not something that automatically exists without good habits. This chapter discusses the fundamental principles of security in Linux, why Linux is relatively more secure compared to other systems, and the role of system updates as our primary defense.
34.1 The Principle of Least Privilege
Least privilege is a principle stating that every user and program should only have access rights limited to what is strictly necessary to perform their tasks. We have encountered this principle previously when discussing sudo, where we run administrative commands only when needed.
In practice, we work with regular user accounts and use sudo for special tasks. Through this approach, if a program or our session is compromised, the damage it can cause remains limited because it does not run with full root privileges.
Interestingly, this principle continues to be strengthened down to the implementation level. Starting from Ubuntu 26.04 LTS, the sudo command we type is actually executed by sudo-rs, a re-implementation of sudo written in Rust for memory safety. For everyday users, nothing changes in terms of usage: the commands, options, and the /etc/sudoers file remain exactly the same. The risk of security vulnerabilities due to memory bugs in legacy C code is significantly reduced. The classic sudo implementation remains available as sudo.ws should it ever be needed for compatibility.
34.2 Why is Linux Relatively More Secure Than Windows?
No system is completely immune, but Linux possesses several characteristics that make it relatively more secure.
- Multi-user design. From the beginning, Linux was designed for multiple users. Every user and process has restricted access permissions, so an issue on one account does not automatically affect the entire system.
- Official package managers. As previously discussed, software is generally installed from official repositories that are curated and signed, drastically reducing the risk of installing malicious programs.
- Open source ecosystem. The Linux source code is open for anyone to inspect. Vulnerabilities can be discovered and fixed quickly by a vast global community.
- Mandatory Access Control (MAC). In addition to the file permissions and ownership we studied earlier, both Ubuntu and Fedora enable an additional security layer that restricts what a program is allowed to do, regardless of which user executes it.
This MAC layer works behind the scenes and has different implementations across the two distros. Ubuntu uses AppArmor, which is active by default and operates based on file paths. For example, a program is only allowed to access specific directories and files according to its profile. Fedora uses SELinux in enforcing mode by default, operating based on security labels attached to every file and process. Both adhere to the same principle, namely "deny by default, allow explicitly," so even if an application is successfully exploited, its impact remains constrained by the active profile or policy. The status of each can be checked with sudo aa-status on Ubuntu, or sestatus on Fedora.
The combination of these four factors makes Linux a harder target for attackers, especially for everyday desktop usage.
34.3 System Updates as Primary Security
One of the most vital security habits is keeping the system updated. Most attacks exploit vulnerabilities that have actually been patched in newer versions, but still exist on unupdated systems.
34.3.1 sudo apt upgrade on Ubuntu
On Ubuntu 26.04 LTS, update the system with the following two commands.
sudo apt update
sudo apt upgrade
The first command refreshes the package list, while the second updates the installed packages.
34.3.2 sudo dnf upgrade on Fedora
On Fedora Workstation 44, use the following command.
sudo dnf upgradeDNF automatically checks repository metadata before updating, so a single command covers both the refresh and update processes. The dnf command we type in Fedora 44 is actually handled by the DNF5 backend, a faster successor to DNF, though basic command syntax like upgrade remains identical to before.
34.4 Automatic Updates
To ensure updates are not forgotten, both distributions provide automatic update mechanisms.
34.4.1 Unattended Upgrades on Ubuntu
Ubuntu features Unattended Upgrades, which can download and install security updates automatically. This feature is generally enabled during installation, particularly for security patches. We can inspect and configure it via the Software & Updates settings under the Updates tab, where automatic security update options are available.
34.4.2 dnf5-automatic on Fedora
Fedora 44 uses DNF5 as its package manager backend, so the packages and systemd units for automatic updates follow DNF5 naming conventions. Install and enable this tool using the following commands.
sudo dnf install dnf5-plugin-automatic
sudo systemctl enable --now dnf5-automatic.timer
The command above installs the dnf5-plugin-automatic plugin and enables the dnf5-automatic.timer systemd timer that runs update checks on a schedule. By default, this plugin only downloads updates; adjust the apply_updates option in the configuration file /etc/dnf/automatic.conf if you want updates to be installed automatically as well, rather than just downloaded.
Security in Linux is built upon a solid design foundation and reinforced by our habits as users. Apply the principle of least privilege, rely on official repositories, leverage the Mandatory Access Control layers that are enabled by default, and keep the system updated. These steps form the most fundamental foundation to keep your desktop secure. In the next chapter, we will delve deeper into account security, including password management and SSH usage.