
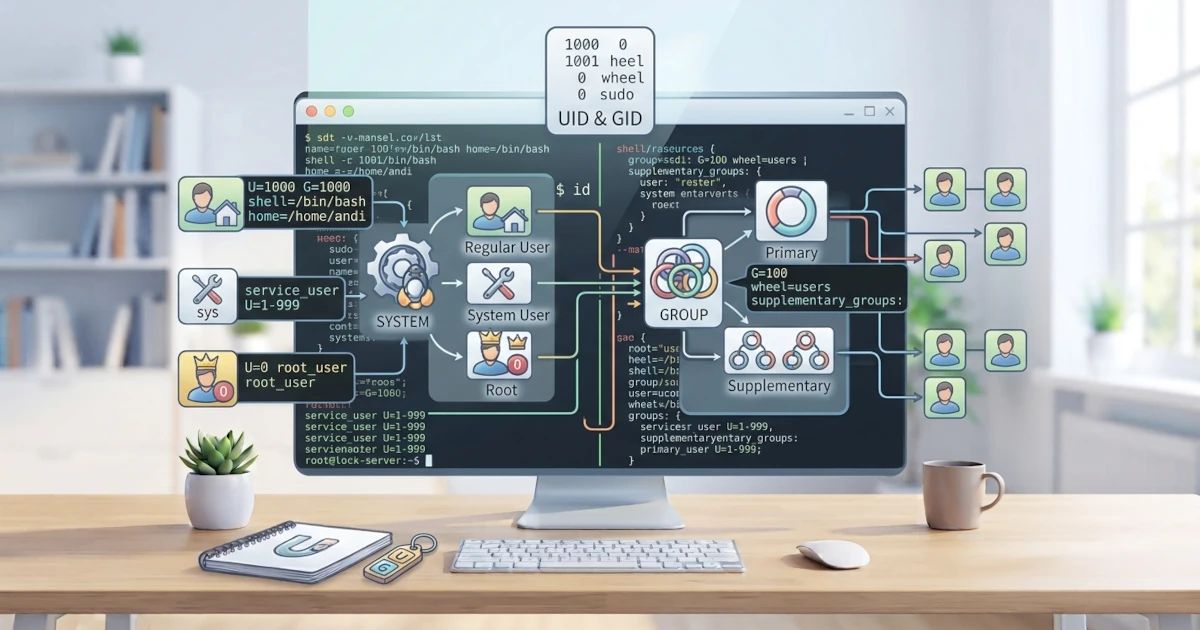
Linux is a multi-user operating system. This means that a single system can be used by multiple people simultaneously, and each person has their own identity and access rights. That identity is represented by the concept of users (user) and groups (group). Understanding both is an essential foundation before we explore file permissions in the next chapter. In this chapter, we will get to know UIDs and GIDs, read user configuration files such as /etc/passwd and /etc/group, and practice commands to add, modify, and delete users and groups, both via the terminal and through the Settings application in GNOME.
21.1 User Concepts in Linux
Every user account in Linux is identified by the system not by name, but by a number called a UID (User ID). Usernames such as andi or siti are merely human-readable labels. When that name is mapped to a number, it is actually the system that uses the number to identify the owner of files, processes, and various other objects.
21.1.1 UID (User ID)
A UID is an integer that is unique to each user. Broadly speaking, the UID range is divided into several groups.
| UID Range | Description |
|---|---|
0 | Root user, full system administrator |
1-999 | System user (system user), used by services |
1000 and above | Regular user (human) |
The first user created during the installation of Ubuntu 26.04 LTS or Fedora Workstation 44 generally receives UID 1000. Subsequent users will obtain UID 1001, 1002, and so on. These boundary limits are controlled by the UID_MIN and UID_MAX variables in the /etc/login.defs file. Check these boundary values using the following command.
grep -E "^UID_MIN|^UID_MAX" /etc/login.defs21.1.2 User Types: Regular User, System User, and Root
- Regular user is an account for humans who use the system daily. This account has its own home directory at
/home/name, for example/home/andi. - System user is an account automatically created by the system to run specific services, such as
www-datafor a web server orsshdfor SSH. This account is not intended for interactive login. - Root is a privileged user with UID
0who holds full authority over the entire system. On modern desktops, we do not log in as root; instead, we use thesudocommand, which will be discussed in the next chapter.
21.1.3 The /etc/passwd and /etc/shadow Files
Basic user information is stored in the /etc/passwd file. Although its name contains the word "password", this file no longer stores passwords, but only account information. Each line represents a single user and consists of seven colon-separated (:) fields.
name:x:UID:GID:info:home:shell| Field | Description |
|---|---|
name | Username |
x | Indicator that the password is stored in /etc/shadow |
UID | User ID |
GID | User's primary Group ID |
info | Additional information, usually full name |
home | Home directory location |
shell | Shell used at login |
Actual passwords are stored in the /etc/shadow file. This file can only be read by root because it contains password hashes as well as password validity and expiration information. Its format also consists of several colon-separated fields.
name:password_hash:last_changed_day:min_age:max_age:warning:grace:expiration:reservedBesides the password hash, the three fields most frequently used by administrators are max_age (the day limit before a password must be changed), warning (how many days in advance a user is reminded to change the password), and expiration (the date the account is completely disabled). This is why regular users only see an x in /etc/passwd instead of the real password.
21.2 Group Concepts
A group is a way to aggregate multiple users so that access rights can be granted collectively. Instead of granting permissions individually to each person, an administrator simply grants permissions to a group, and all its members automatically receive those permissions.
21.2.1 GID (Group ID)
Just like users, groups are also identified by a number called a GID (Group ID). The GID range follows a pattern similar to UIDs.
| GID Range | Description |
|---|---|
0 | Group root, the primary group belonging to the root user |
1-999 | System group, used by services (e.g., www-data, sshd) |
1000 and above | Regular group, including each user's personal group and administrator-created groups |
Every user must belong to at least one group known as the primary group. This group is usually created automatically with the same name as the username. In addition to the primary group, a user can also be a member of one or more supplementary groups (secondary groups).
21.2.2 Primary Group and Supplementary Group
- Primary group is the user's main group. When a user creates a new file, that file is automatically owned by the user's primary group.
- Supplementary group is an additional group to which the user belongs, such as the
sudogroup on Ubuntu, thewheelgroup on Fedora, or thelibvirtgroup for virtualization.
The distinction between the two is important when managing file permissions, because the group that owns a newly created file is determined by the primary group.
21.2.3 The /etc/group and /etc/gshadow Files
The list of groups is stored in the /etc/group file. Each line represents a single group and consists of four fields.
name:x:GID:members| Field | Description |
|---|---|
name | Group name |
x | Group password indicator |
GID | Group ID |
members | List of supplementary members, comma-separated |
Note that the members field in /etc/group lists only supplementary members of that group. Users who have that group as their primary group will not be listed in this field, as their membership is already determined via the GID field in /etc/passwd. Meanwhile, the /etc/gshadow file stores group passwords and the list of group administrators. Like /etc/shadow, this file can also only be read by root.
21.3 Viewing User Information
Several simple commands help us discover our identity on the system.
| Command | Function |
|---|---|
whoami | Displays the current username |
id | Displays UID, GID, and all groups for the user |
groups | Displays the list of groups of which the user is a member |
The whoami command answers the most basic question: "who am I logged in as?". The id command is more comprehensive, as it displays the UID, primary GID, and all supplementary groups simultaneously. Run id without arguments to view your own information, or id username to view another user's information.
idThe groups command focuses solely on group membership, making it useful when we want to check if an account already belongs to a specific group. If at any point we need to look up a specific line in /etc/passwd or /etc/group without manually opening the file, the getent passwd username or getent group groupname commands can also be used. Both read active user identity sources on the system, including when the system connects to a centralized directory such as LDAP.
21.4 User Management (Commands)
To manage user accounts from the terminal, administrative privileges are required, so each command is preceded by sudo.
21.4.1 useradd and adduser: Adding Users
There are two commands to add users. useradd is a low-level command available across all distributions, but its parameters are rather lengthy. Meanwhile, adduser is a more user-friendly wrapper script. On Ubuntu, adduser is interactive and guides us through setting a password and entering user details, whereas on Fedora, adduser is merely a symbolic link to useradd, making its behavior identical to useradd.
# on Ubuntu 26.04 LTS
sudo adduser budi

# on Fedora Workstation 44
sudo useradd -m budi
sudo passwd budi
The -m option in useradd forces the creation of a home directory. Its default behavior varies between distributions: on Ubuntu, the default value of CREATE_HOME in /etc/login.defs is no, requiring -m to be included for the home directory to be created. On Fedora, CREATE_HOME defaults to yes, so the home directory is created even if -m is omitted. Nevertheless, explicitly including -m is recommended to keep commands consistent and portable across distributions.
After a new user is created, make it a habit to verify it with id budi or getent passwd budi. This practice ensures that the UID, GID, and home directory are properly recorded before moving on to subsequent configurations.
21.4.2 usermod: Modifying User Attributes
The usermod command is used to modify existing user attributes. Frequently used options include the following.
| Option | Function |
|---|---|
-aG group | Appends the user to a supplementary group (append) |
-l new_name | Changes the login name |
-d /path/home | Changes the home directory location recorded in /etc/passwd |
-m | Used with -d to move existing home directory contents to the new location |
-s /bin/bash | Changes the login shell |
Pay close attention to the -a (append) option. Without -a, the -G option will overwrite the user's entire supplementary group list, causing them to lose existing group memberships. Also note that -d without -m only updates the home location record in /etc/passwd without moving existing files from the old home directory.
sudo usermod -aG sudo budiThe command above adds budi to the sudo group on Ubuntu, enabling administrative command execution.
21.4.3 userdel: Deleting Users
The userdel command removes a user account. By default, the user's home directory is not deleted. Use the -r option to delete the account along with its home directory and mail spool.
sudo userdel budi
sudo userdel -r budi
On Ubuntu, the package containing adduser also provides deluser as its counterpart, which is functionally equivalent to userdel but offers beginner-friendly defaults, such as sudo deluser --remove-home budi.
In practice, userdel sometimes fails with an error message like userdel: user budi is currently used by process 1234. This happens because the user still has an active login session or running processes on the system, such as an unclosed terminal session. Ensure the user has completely logged out or terminate those processes using pkill -u budi before attempting to delete the account again.
21.4.4 passwd: Managing Passwords
The passwd command changes a user password. Run it without arguments to change your own password, or supply a username to change another user's password (requires sudo).
passwd
sudo passwd budi
21.5 Group Management
Just like users, groups can also be managed using dedicated commands.
| Command | Function |
|---|---|
groupadd | Adds a new group |
groupmod | Modifies group attributes |
groupdel | Deletes a group |
gpasswd | Manages group members and group passwords |
21.5.1 groupadd, groupmod, groupdel
sudo groupadd developer
sudo groupmod -n dev developer
sudo groupdel developer
The example above creates the developer group, renames it to dev using the -n option, and then deletes it. A group can only be deleted if it is no longer the primary group for any user. On Ubuntu, the delgroup command is available as an alternative to groupdel, aligning with the adduser/deluser pair.
To ensure a group is properly registered in the system, run getent group dev and verify that the GID and members match expectations.
21.5.2 gpasswd: Managing Group Members
The gpasswd command is the most convenient way to add or remove members from a group.
sudo gpasswd -a budi developer
sudo gpasswd -d budi developer
The -a option adds a member, while -d removes a member. After group membership changes, users typically need to log out and log back in for changes to take effect in active sessions.
21.6 User Management via GUI Settings
If you prefer a graphical interface, GNOME 50 provides user settings through the Settings application. Open the System panel, then select Users. Here, you can add new users, set profile pictures, change passwords, and choose the account type, either Standard or Administrator. You can also enable Automatic Login and view the system language configured for each user.
Keep in mind that certain administrative changes, such as creating new users or changing passwords for other accounts, still require administrative authentication. This GUI panel displays existing users and allows account deletion with a few clicks. The same panel is available in Ubuntu 26.04 LTS and Fedora Workstation 44, as both utilize GNOME.
Understanding users and groups is the first step toward managing system access in Linux. Once you can create accounts, modify their attributes, and manage group memberships, you have established the necessary foundation to understand file permissions. In the next chapter, we will learn how regular users execute administrative tasks using sudo, and how read, write, and execute permissions apply to files and directories.